Your Password Isn't the Weak Point Anymore — Why Cookie Theft Is a Bigger Threat
 Sep 13, 2026
•
 NodeToLearn Expert
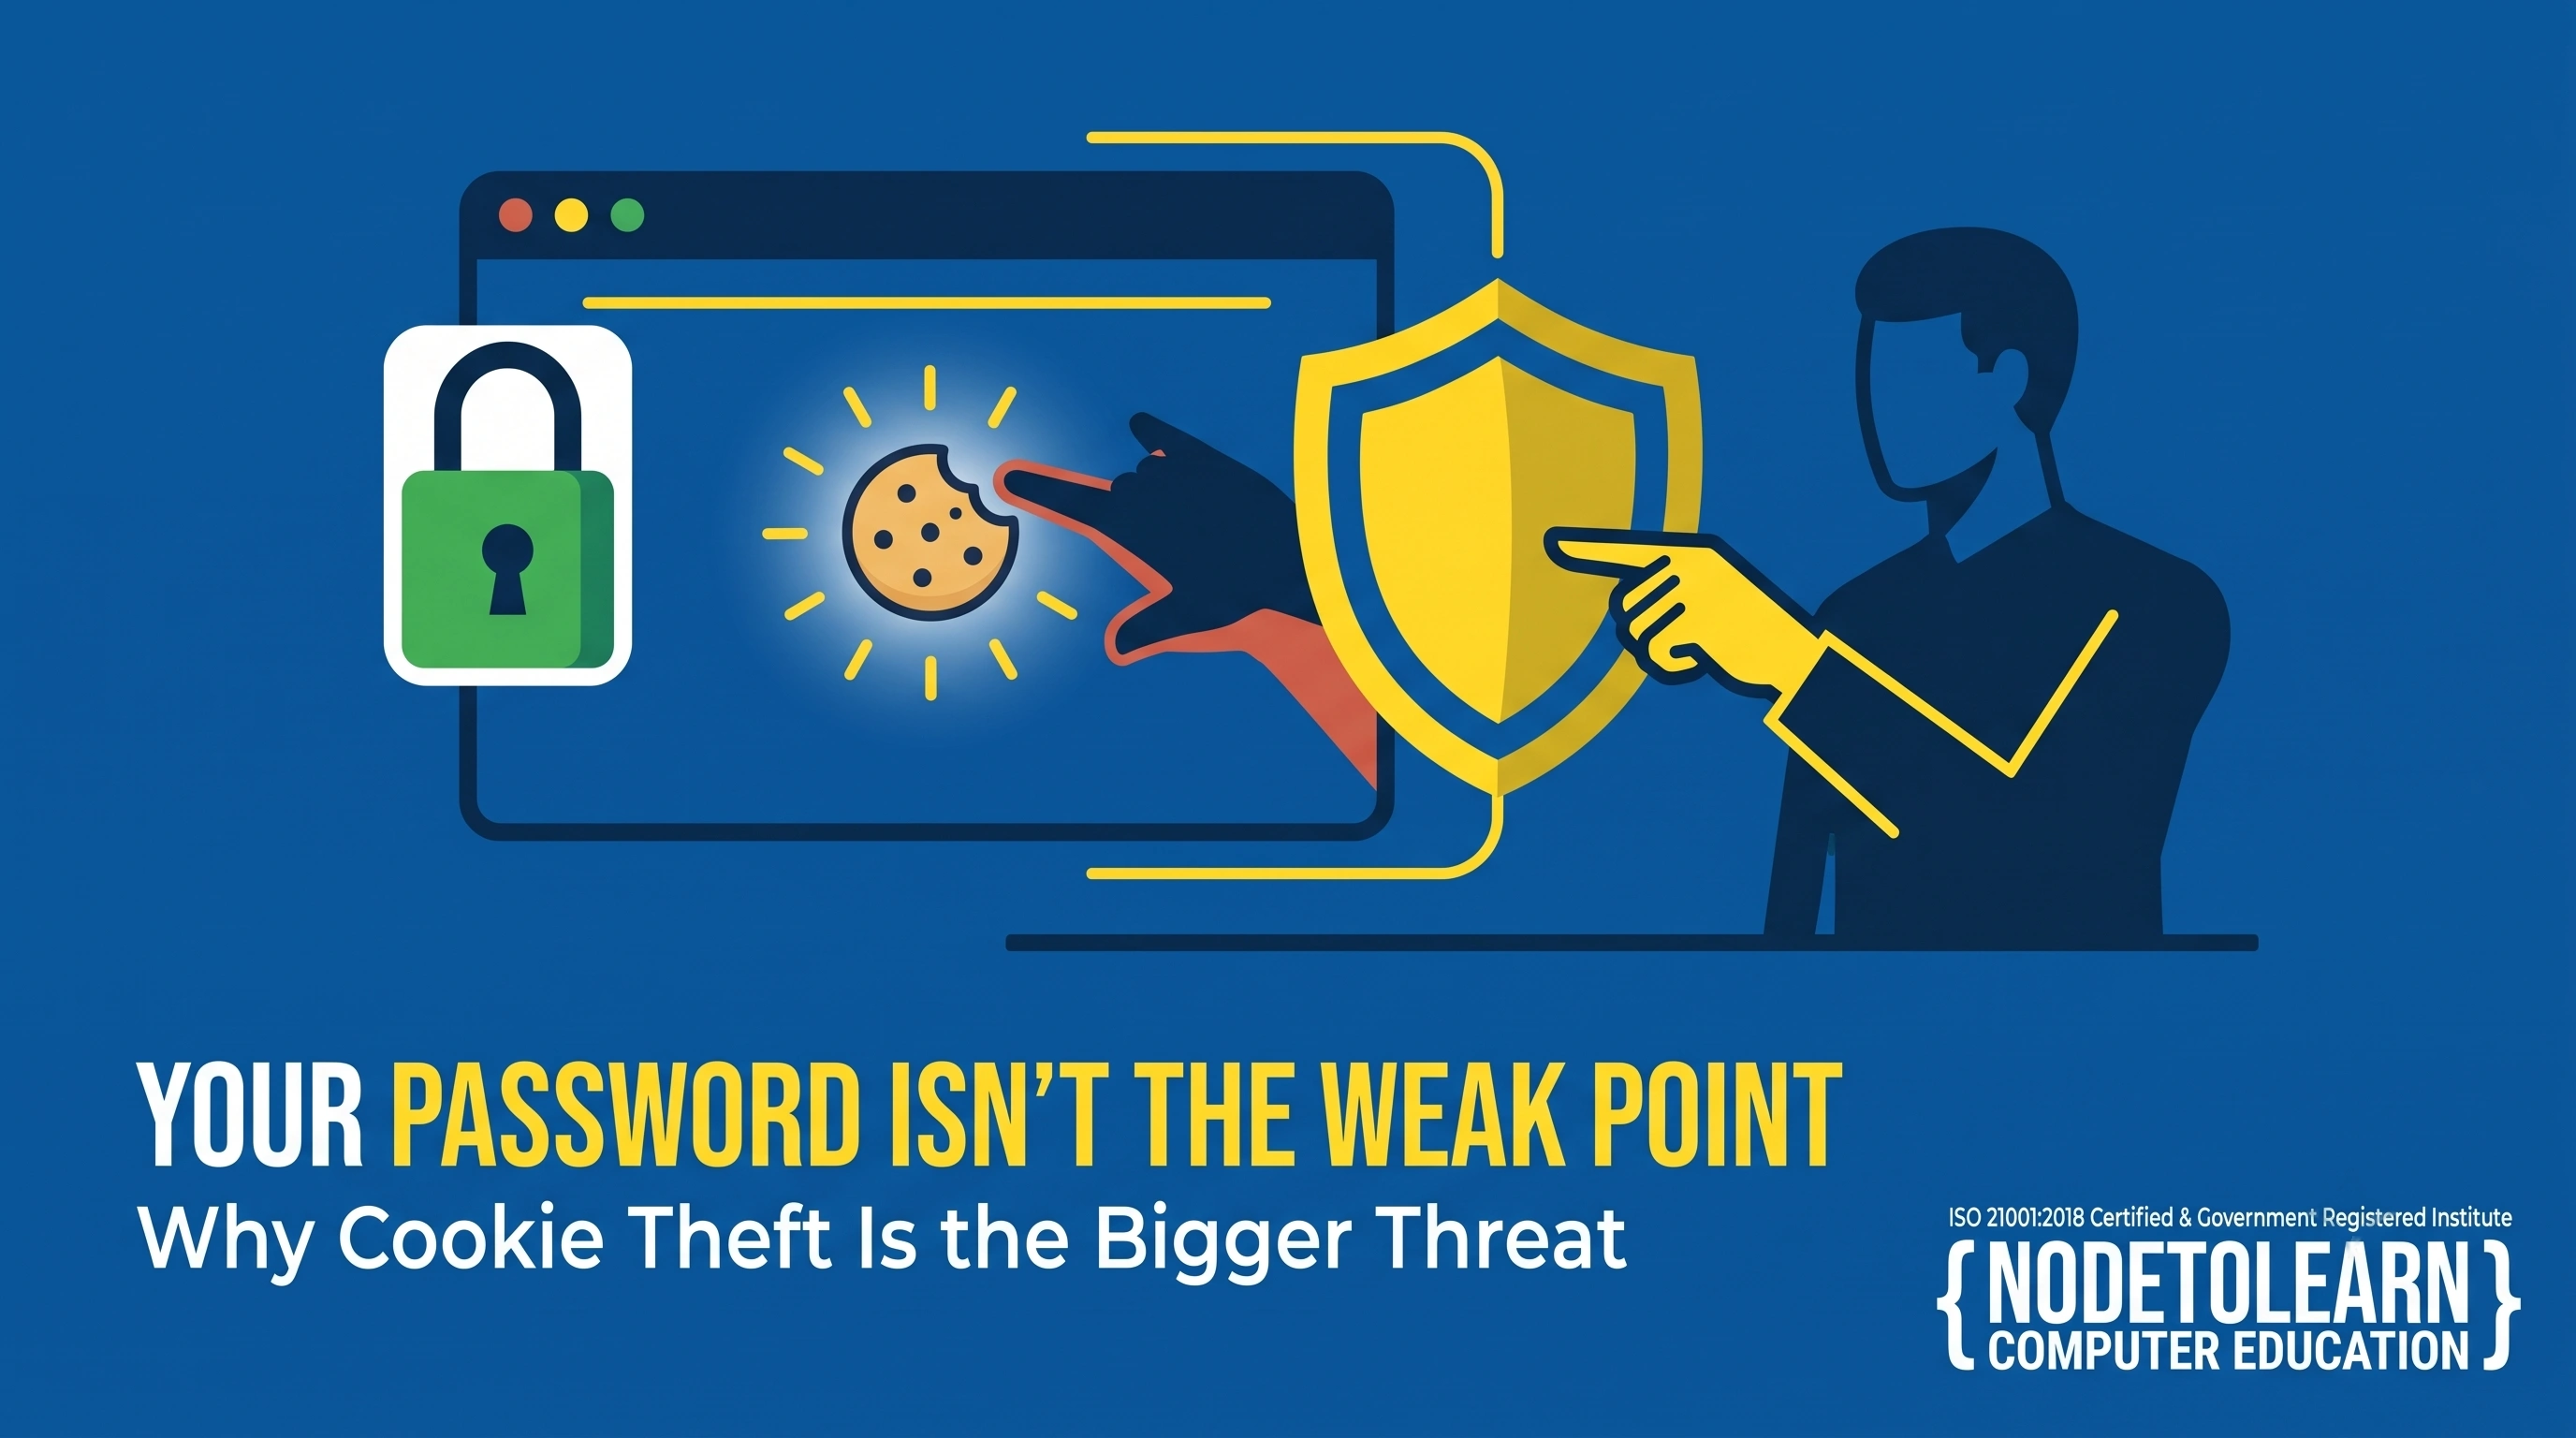
Quick Answer: Security researchers are increasingly warning that stolen authentication cookies — the small files that keep you logged into a website — have become more valuable to cybercriminals than stolen passwords. A stolen cookie can let an attacker access an account without ever needing a password or triggering a login alert. NodeToLearn's Cyber Security course in Nanpura, Surat covers exactly this kind of modern, practical threat, not just outdated password-focused security concepts.
Why Cookies Have Become a Bigger Target Than Passwords
When you log into a website, it typically stores a small authentication cookie in your browser so you don't have to re-enter your password every time. That cookie proves to the website "this person is already logged in." The problem: if an attacker steals that cookie — through malware, a compromised browser extension, or a phishing attack — they can use it to access the account directly, completely bypassing the password and often without triggering typical login security alerts like two-factor authentication prompts.
Why This Matters More Than It Sounds
- Two-factor authentication doesn't always help. If an attacker has a valid session cookie, they've effectively skipped the login process entirely, meaning the extra security of 2FA at login never gets triggered.
- Password changes alone might not stop the attack. If a stolen cookie remains valid, changing your password doesn't necessarily end an attacker's access to an already-active session.
- It's harder for users to notice. Unlike an obvious failed login attempt, cookie-based account takeover can look like normal, ongoing account activity from the platform's perspective.
What This Means for Businesses and Students Learning Security
This kind of threat represents exactly why modern cybersecurity training needs to go beyond "use a strong password" advice. Understanding session management, cookie security, and how modern web authentication actually works has become essential knowledge — not an advanced topic reserved for specialists, but foundational understanding for anyone taking security seriously.
What NodeToLearn's Cyber Security Course Covers Here
- Session & cookie security fundamentals — understanding how authentication actually works beyond just passwords
- Common attack vectors — how cookies get stolen through malware, phishing, and compromised browser extensions
- Defensive practices — secure cookie configuration, session timeout policies, and monitoring for suspicious session activity
- Practical, current threat awareness — training built around how attacks actually happen today, not outdated textbook scenarios
Why This Kind of Practical Knowledge Matters for a Real Career
A cybersecurity candidate who can explain session hijacking and cookie security in an interview demonstrates genuinely current knowledge — a meaningful signal to employers that training wasn't limited to basic, outdated concepts. This is exactly the kind of practical, up-to-date understanding NodeToLearn's hands-on approach is built to produce.
Does changing my password protect me from cookie theft?
Not necessarily on its own — if a stolen session cookie remains active, an attacker may retain access until the session is specifically invalidated, which is why understanding session security matters beyond password hygiene alone.
Is this an advanced topic, or something covered early in cybersecurity training?
Session and cookie security fundamentals are covered as core, practical knowledge within NodeToLearn's Cyber Security course, not treated as an advanced or optional topic.
Does two-factor authentication protect against this kind of attack?
2FA protects the login process itself, but a stolen active session cookie can bypass that step entirely, which is why session-level security practices matter as a separate layer of defense.
Does NodeToLearn offer a free demo for the Cyber Security course?
Yes, a free 3-day demo is available so you can experience the hands-on teaching approach before enrolling.
Learn Security Threats That Actually Matter Today
Book your free 3-day demo at NodeToLearn Computer Education, Nanpura, Surat, and go beyond outdated password-only security training.
Claim Your Free Trial


Frequently Asked Questions
Got questions? We've got answers. Explore everything you need to know about starting your tech career with NodeToLearn.
Still have questions?
Contact Our Team